Decides and responds locally
Sensors, detection, models, decisions, and response remain inside the mission boundary—even when WAN, DNS, or SATCOM fails.
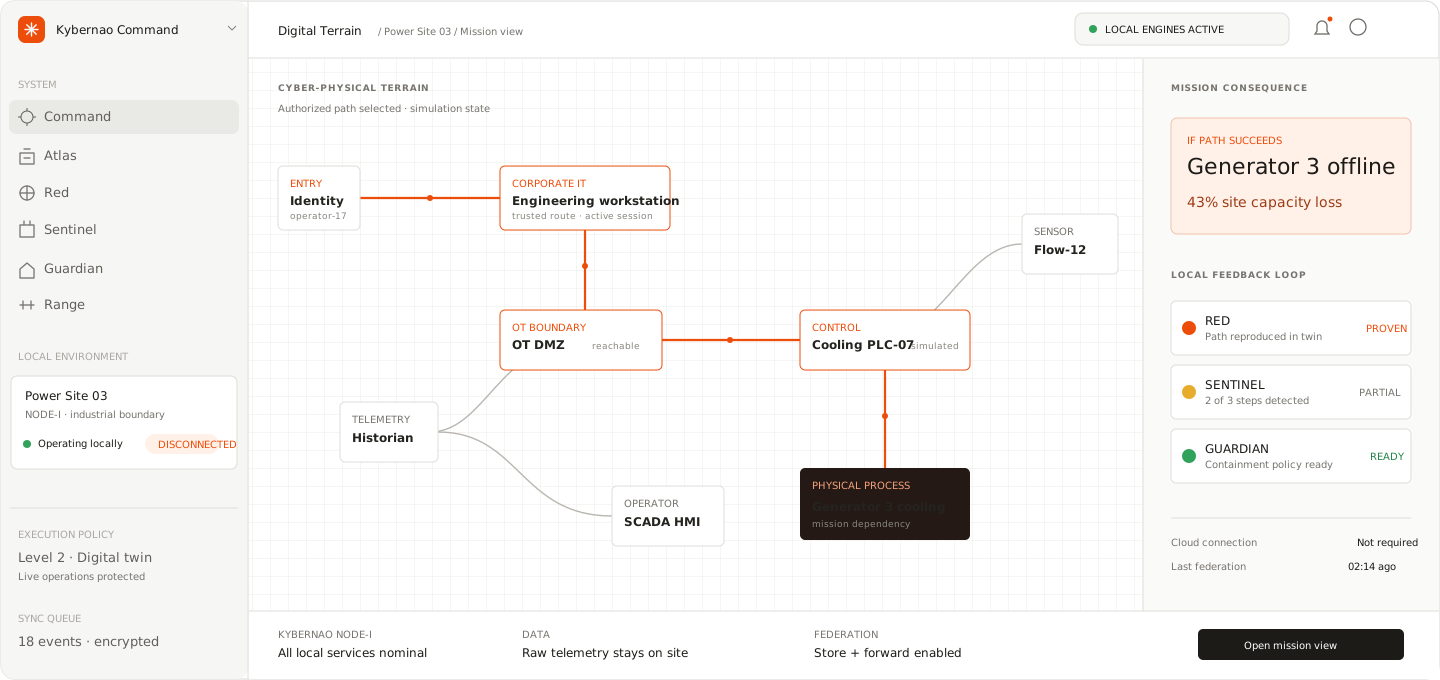
Kybernao keeps operating when connectivity disappears.
Cloud enhanced. Never cloud dependent.
Sensors, detection, models, decisions, and response remain inside the mission boundary—even when WAN, DNS, or SATCOM fails.
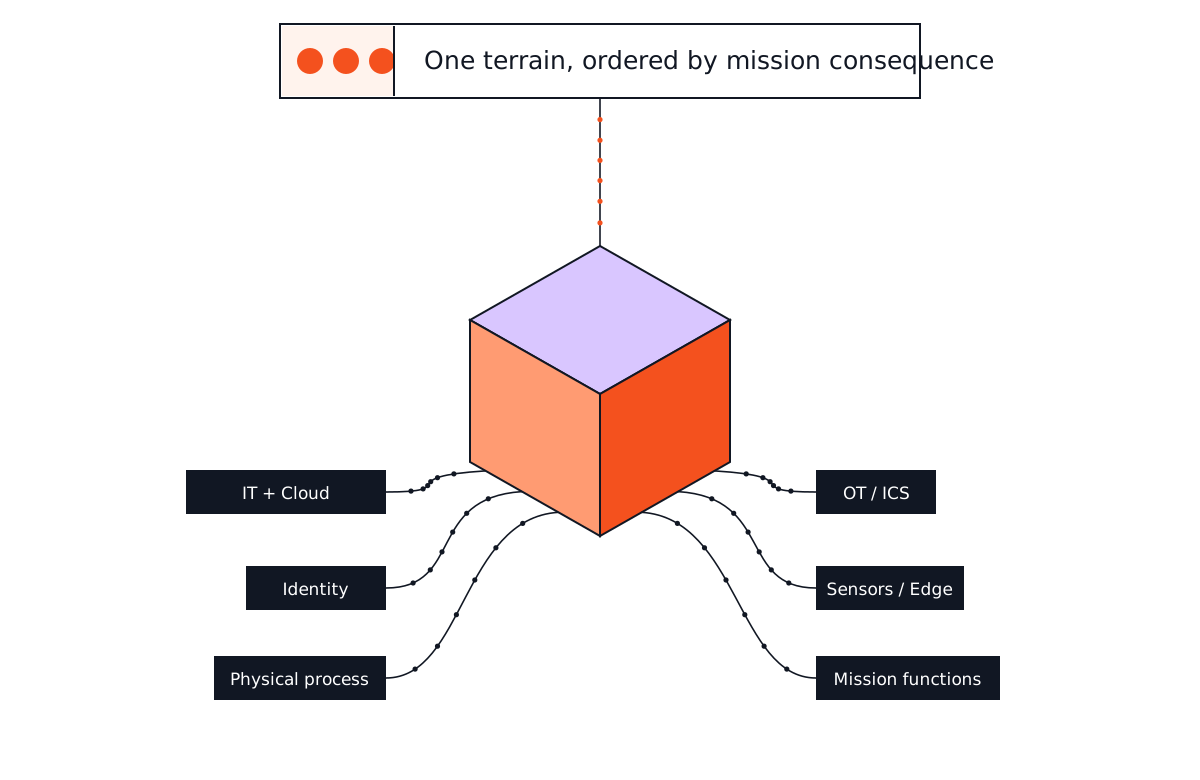
IT, OT, IoT, vehicles, radios, sensors, physical processes, and mission functions resolve into one cyber-physical graph.
Every node operates independently, then exchanges selected state and threat intelligence when bandwidth becomes available.
Cloud-dependent security and disconnected-first infrastructure
One continuous mission-survivability loop
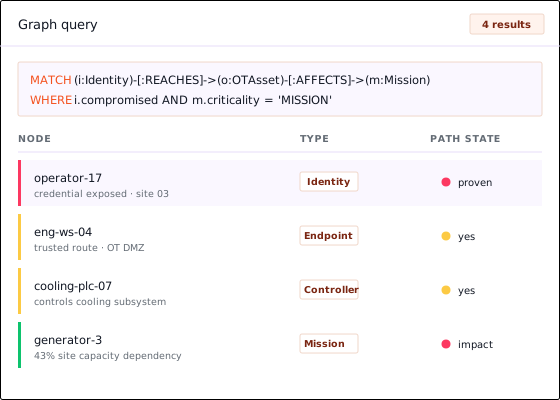
People, identities, applications, networks, radios, sensors, PLCs, vehicles, facilities, and mission functions become nodes in one continuously updated graph.
Kybernao understands what can reach, trust, control, and depend on everything else.
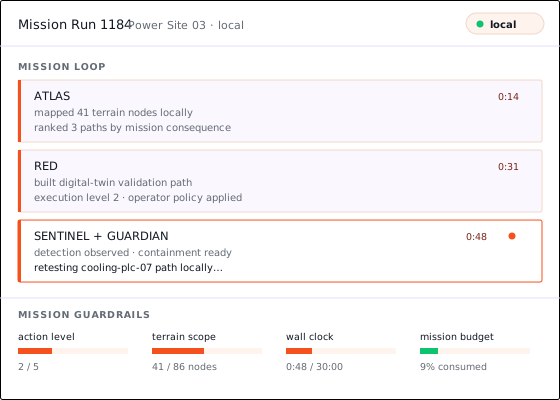
Kybernao Red moves from observation and simulation through digital-twin and non-destructive live validation under explicit execution controls.
Operators see the route, the affected physical process, and the mission consequence before authorizing higher-risk actions.
Authorized adversary telemetry measures whether defenses saw the path and whether local containment can preserve the operation.
After remediation, Kybernao retests the original route. The metric is no longer alert count—it is whether the system survives adversarial pressure.
Kybernao Node puts the cyber system inside the mission boundary.
Compute, models, graph, telemetry, identity, and response in one deployable system.
CPU/GPU/NPU compute, secure hardware root, encrypted storage, passive network interfaces, local models, local APIs, and an offline management plane.
NODE-S tactical · NODE-R rack/datacenter · NODE-I industrial/OT · NODE-X rugged expeditionary.
Kybernao maps how digital systems, physical systems, and mission functions depend on one another.
Cyber infrastructure that travels with the operation.
Map attack paths from enterprise identity through the OT boundary to generation, transmission, and safety-critical processes.
Passive OT visibility, safe digital-twin validation, and local defense for factories and process environments.
Operate across denied, degraded, intermittent, and limited connectivity without centralized reach-back.
Protect data centers, bases, transportation, water, and other environments where disruption becomes physical consequence.
Every Kybernao environment remains sovereign and useful before, during, and after disconnection.
One distributed runtime connecting cyber terrain, adversarial testing, defense, and the operational picture.
Built on Kybernao Fabric →Deployable cyber compute that carries the platform into the site, vehicle, network, or mission.
The cyber-physical and mission graph connecting assets, trust, control, dependency, and consequence.
Authorized adversary emulation with execution levels designed for safety-critical environments.
Local detection informed by the exact paths Kybernao safely validates against the environment.
Autonomous containment and response governed by operator policy and mission constraints.
Digital twins and isolated ranges for validating higher-risk paths without touching live operations.
The operational cyber picture for operators, defenders, leaders, and mission owners.
A secure federated mission layer for exchanging selected state across sovereign Kybernao nodes.
Map one site, operational environment, or tactical mission with us.
Start the architecture session →